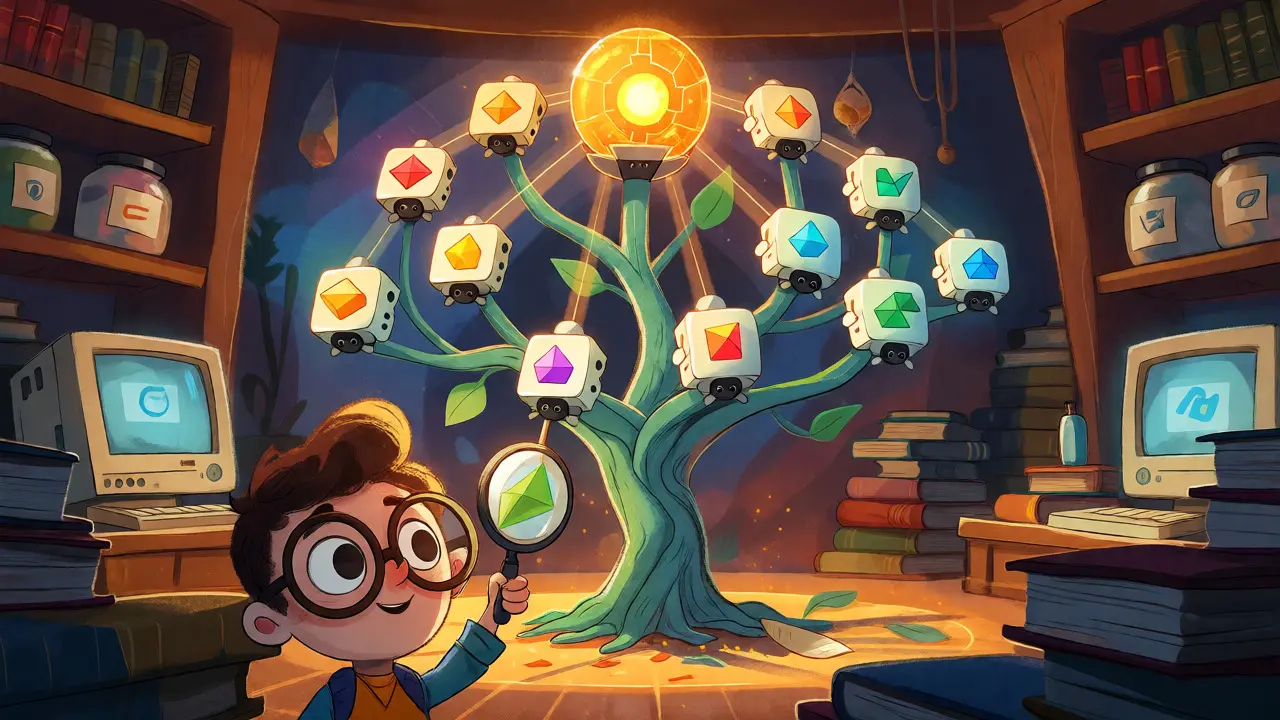
Imagine trying to verify the integrity of a billion transactions without downloading the entire history. Sounds impossible? Not if you understand Merkle trees. These cryptographic structures are the unsung heroes keeping blockchains like Bitcoin and Ethereum secure and efficient. They allow computers to check if data has been tampered with by looking at just one small fingerprint, rather than reading every single byte.
What Exactly Is a Merkle Tree?
A Merkle tree, also known as a hash tree, is a specific type of data structure where every leaf node contains the cryptographic hash of a data block, and every non-leaf node contains the hash of its child nodes. Developed by Ralph Merkle in 1979, this structure creates a hierarchical map of your data. Think of it like a family tree, but instead of names, each person holds a unique code derived from their parents' codes. If any great-grandchild changes their name (data), the code of every ancestor up to the root changes too. This makes detecting changes incredibly easy.
The magic lies in the cryptographic hash function. This algorithm takes an input of any size and produces a fixed-size string of characters, which appears random. Even changing one bit in the original data results in a completely different hash output. When you combine these hashes pairwise up the tree, you eventually reach a single top-level hash called the Merkle root. This root acts as the definitive fingerprint for the entire dataset.
Core Security Properties That Matter
Why do developers obsess over this structure? It comes down to four main security advantages that solve real-world problems in distributed systems.
- Data Integrity Verification: You can prove data hasn't changed without sharing the whole dataset. If the calculated Merkle root matches the expected root, the data is intact.
- Efficient Storage Usage: Storing just the root hash requires minimal disk space compared to storing full transaction histories, yet it maintains full cryptographic security.
- Bandwidth Reduction: Verifying a single transaction only requires sending a small "proof" path through the tree, not the entire block. This saves massive amounts of network bandwidth.
- Fast Validation: Checking integrity happens almost instantly. Instead of scanning gigabytes of data, a computer performs a few logarithmic calculations.
This efficiency is critical for lightweight clients, often called SPV (Simplified Payment Verification) nodes. These devices, like mobile wallets, don't store the whole blockchain. They rely on Merkle proofs to confirm that a specific transaction exists within a block without trusting the full node they connect to blindly.
The Power of Membership Proofs
One of the most practical applications of Merkle trees is the ability to generate membership proofs. This property allows you to verify that a specific element is part of a larger set without revealing the rest of the set. Imagine a database of authorized users. Instead of sending the entire list to check if Alice is allowed in, the system sends a small proof showing Alice's position in the tree and the necessary sibling hashes to reconstruct the root.
This minimizes information exposure. In access control systems, this means you don't leak who else is authorized. For large datasets, such as NFT collections on Solana, this reduces costs significantly. By using state compression techniques involving Merkle trees, minting one billion tokens can cost 507 SOL instead of 12,000,000 SOL. The math scales beautifully: verification time grows logarithmically with the size of the dataset. So, even if your data doubles, the effort to verify it barely increases.
Integration with Zero-Knowledge Proofs
Merkle trees aren't just about checking existence; they play a key role in privacy-preserving technologies like Zero-knowledge proofs (ZKPs). ZKPs allow one party to prove they know a value without revealing the value itself. When combined with Merkle trees, these systems can prove that a user possesses certain attributes or funds without exposing their entire balance or identity.
For example, in confidential cryptocurrency transactions, a Merkle tree can hide the specific inputs being spent while still proving they are valid and unspent. This integration enhances privacy in identity verification protocols and confidential databases. Tools like cuPQC leverage these structures to create efficient proof systems, ensuring that security doesn't come at the expense of performance.
Real-World Impact on Blockchain Architecture
Without Merkle trees, modern blockchains would struggle under their own weight. Consider Bitcoin. Every block contains thousands of transactions. Without a Merkle root, verifying a new block would require downloading and hashing every single transaction again. Nodes would need massive storage and computing power. With Merkle trees, a node only needs to download the block header, which includes the Merkle root, and then request specific transaction proofs as needed.
This separation of proof from data is fundamental. It allows for scalable networks where light clients can interact securely with heavy-duty servers. It also enables features like fast syncing for new nodes joining the network. They can start with just the headers and gradually fill in details, knowing exactly when a piece of data is verified against the canonical root.
Security Limitations and Future Challenges
No technology is perfect. While Merkle trees are robust, they have limitations. First, their security depends entirely on the underlying hash function. If a weakness is found in SHA-256 or Keccak, the entire tree becomes vulnerable. Second, there is the looming threat of quantum computing. Current hash functions might be susceptible to attacks from powerful quantum computers, potentially breaking collision resistance.
Additionally, while Merkle trees hide data content, the structure itself can sometimes reveal patterns. Analyzing the shape of the tree or the frequency of updates might give insights into usage patterns or relationships between data points. To combat this, researchers are exploring post-quantum cryptography and adding blinding factors to mask structural analysis.
| Feature | Traditional Verification | Merkle Tree Verification |
|---|---|---|
| Data Required | Full Dataset | Root Hash + Proof Path |
| Storage Cost | High (Linear growth) | Low (Logarithmic growth) |
| Verification Speed | Slow (O(n)) | Fast (O(log n)) |
| Privacy | Low (Exposes all data) | High (Only proves membership) |
| Network Load | Heavy | Minimal |
Practical Implementation Tips
If you're building with Merkle trees, keep a few things in mind. Pre-determine the tree depth. In systems like Solana's concurrent Merkle trees, the maximum depth affects account allocation costs. Deeper trees offer more flexibility but require more initial setup resources. Use specialized libraries, such as @solana/spl-account-compression, to handle the complex math and state management.
Also, consider caching. Storing intermediate hashes (canopy depth) can speed up repeated verifications, though it uses more memory. Balance your need for speed against available resources. Always validate your implementation against known test vectors to ensure your hashing logic aligns with standard specifications.
What is a Merkle root?
The Merkle root is the single hash value at the top of a Merkle tree. It represents the cryptographic fingerprint of all the data blocks contained within the tree. If any single piece of data changes, the Merkle root changes completely, allowing for instant detection of tampering.
How do Merkle trees save bandwidth in Bitcoin?
Instead of downloading every transaction in a block to verify one payment, a lightweight client requests a Merkle proof. This proof consists of a few hashes along the path from the transaction to the root. This method drastically reduces the amount of data transmitted over the network compared to downloading the full block.
Are Merkle trees secure against quantum computers?
Current implementations use classical hash functions like SHA-256, which may be vulnerable to future quantum attacks. However, research is ongoing into post-quantum cryptographic hash functions. Integrating these quantum-resistant algorithms into Merkle tree structures is a key area of development to ensure long-term security.
Can Merkle trees hide private data?
Yes, through membership proofs. You can prove that a specific item exists in a dataset without revealing the other items. This is useful for privacy-focused applications, such as proving you have enough funds for a transaction without revealing your total balance, especially when combined with zero-knowledge proofs.
What happens if two transactions have the same hash?
This is known as a hash collision. Cryptographic hash functions are designed to make collisions computationally infeasible. If a collision occurred, it could compromise the integrity of the Merkle tree. However, with strong algorithms like SHA-256, the probability of this happening by chance is astronomically low.
